Several companies, one site: keeping the network and access separate
A shared internet connection and firewall, separate networks and a Microsoft 365 tenant for each company. What is shared, what stays separate, how costs are split and where such projects are most likely to snag.
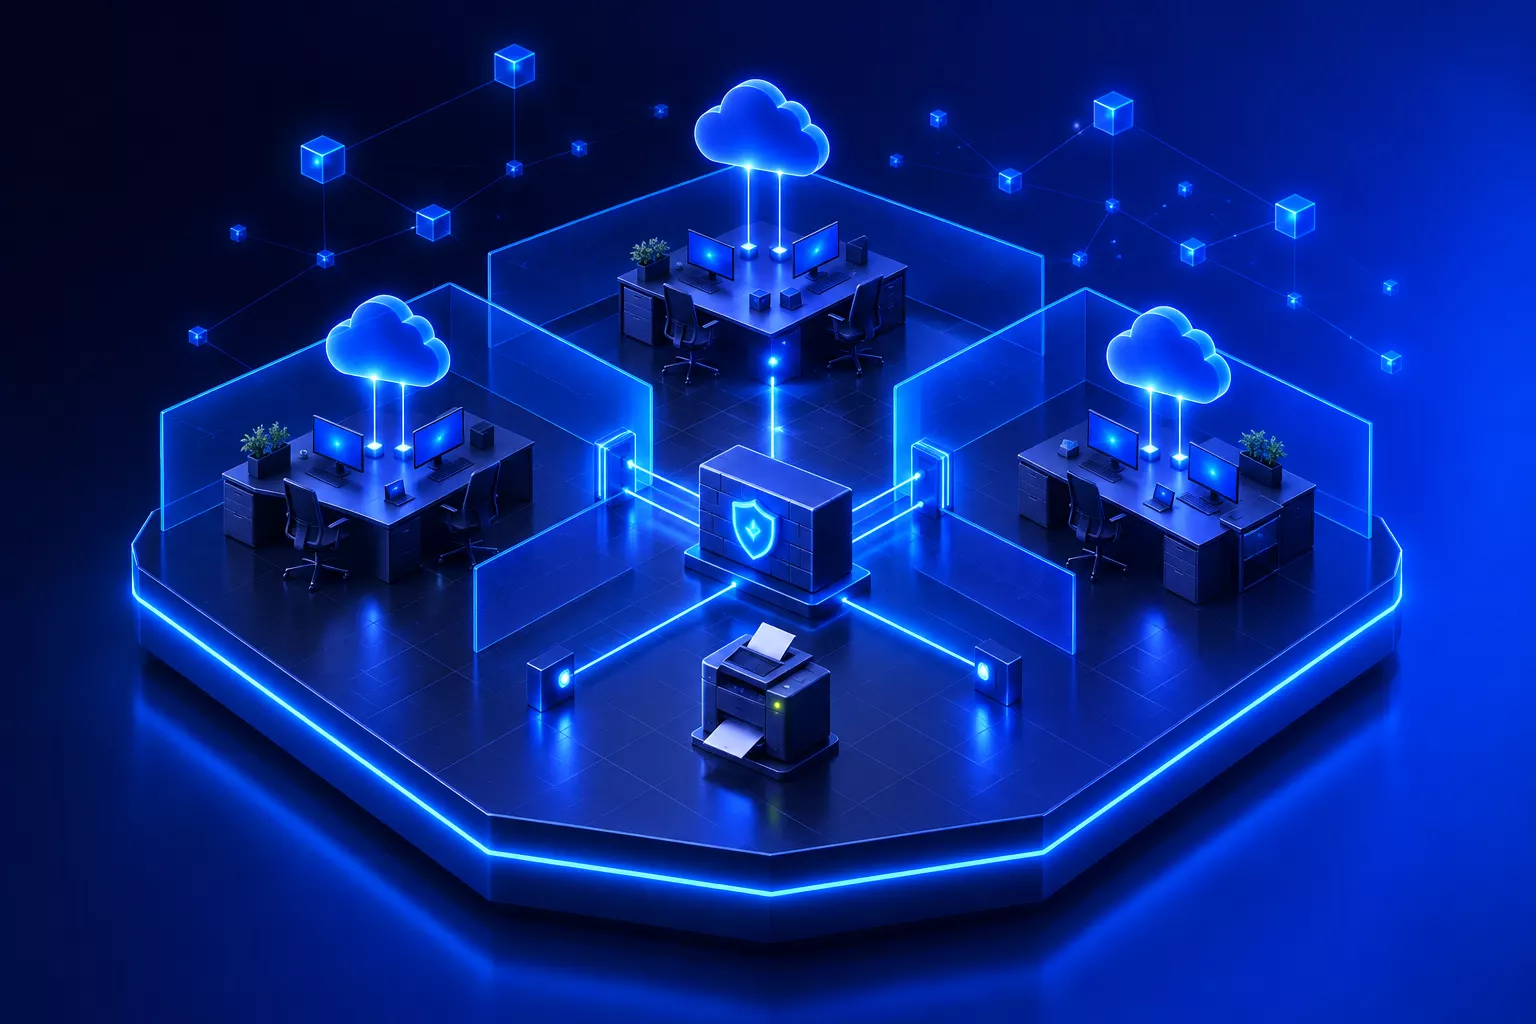
When several companies share premises and an internet connection, responsibilities and access rights still need to be clearly defined. Using a 2024 project with four companies in one group, I show how I planned the shared network and kept each company’s part of it separate.
The starting point
A group with several companies, all at the same site. Over the years the companies grew into one shared network: one connection, one network, every computer able to see every other. Email ran with a web host and line-of-business software sat on local machines. Who was allowed to see which data was more a matter of habit than of design.
As long as everything works, hardly anyone notices. At the latest when a company is sold, restructured or audited, the habit becomes a problem. The same goes for malware on a computer in one company.
What is shared and what stays separate
Internet connection, firewall, switches and Wi-Fi infrastructure. Plus devices that several companies genuinely use together, such as printers or the phone system.
Each company has its own network segment and its own Microsoft 365 tenant with its own accounts, mailboxes and file storage. What a company can see is its own decision.
The firewall decides which traffic is allowed between the segments. The default is nothing, except what is explicitly needed.
I split shared infrastructure and shared effort between the companies, according to a key the group sets in advance.
A network segment for each company
Technically, VLANs handle the separation. The firewall decides whether and how traffic may flow between the networks, not the accident of how the cabling was done. VLANs on their own do not protect anything: only the firewall rules determine what may pass between the networks.
Germany’s Federal Office for Information Security (BSI) addresses this in its IT baseline protection guidance. For VLANs of different organisations on one switch, it recommends physical separation or encrypting the data. For a group whose companies work closely together and share an owner, separation through VLANs and firewall rules is often appropriate. How far the separation has to go depends on how sensitive the data is. The group should settle that before the planning, not afterwards.
A separate Microsoft 365 tenant for each company
One shared tenant for all companies looks simpler at first glance, and separate tenants are not a legal requirement. They do fit better with what the companies are in legal terms, though: independent entities with their own data, their own licences and their own responsibility. If a company is later sold or wound up, its tenant goes over as a whole. Nobody has to untangle accounts and files from a shared environment.
Where staff work across companies, Microsoft’s multitenant organisation capabilities offer ways to connect tenants without merging them.
Shared devices
Printers and the phone system are where the separation needs exceptions. Here the firewall lets computers from every company reach the shared printer. That does not open a path into the other companies’ networks. The phone system sits in its own segment. That alone does not guarantee call quality: it also takes QoS rules that give voice traffic priority on the switches and at the internet connection.
How are the costs shared?
Shared infrastructure means shared effort, both during set-up and in day-to-day operation. I bill this effort split between the companies. The group decides which key applies, by workstation for example or in equal shares. What matters is that it is settled before work begins. Negotiating afterwards over who pays what share of a firewall is unpleasant for everyone involved.
Where do projects like this usually snag?
The technology in projects like this is quite manageable. It gets more involved when requirements only become known after the work is done: one company needs access to another’s files, a device is to be used by everyone, or a workstation moves to a different company. Because the rules, segments and permissions are already in place by then, each of these changes means extra work.
That is why, before planning, I talk to each company separately about who works with whom and which data has to stay separate. Shared printers, telephony and any future tenants of the building are included from the start. I put the result in writing and have every company confirm it.
Questions before several companies share one network
- Which companies actually work together? And on which data?
- Which devices are shared? Printers, phone system, meeting rooms, scanners.
- How sensitive is each company’s data? That determines how far the separation has to go.
- Who decides for each company? One contact per company saves many rounds of coordination later.
- What key is used to split costs?
- What happens when a company joins or leaves the group?
Frequently asked questions
Can several companies share one internet connection and one firewall?
Yes, if each company gets its own network segment (VLAN) and the firewall controls which traffic may pass between the segments. Without an explicit rule, it lets nothing through.
Do the companies in a group need separate Microsoft 365 tenants?
There is no requirement to do so. I recommend a separate tenant for each company, because that fits independent entities with their own data, licences and responsibility. If the group later sells a company, its tenant goes over as a whole. For staff who work across companies, Microsoft offers ways to connect tenants without merging them.
Is separation through VLANs enough, or do the networks need to be physically separate?
It depends on how sensitive the data is. For VLANs of different organisations on one switch, Germany’s Federal Office for Information Security (BSI) recommends physical separation or encrypting the data. For a group whose companies work closely together and share an owner, VLANs and firewall rules are often appropriate.
Sources
- Separating network segments, VLANs of different organisations: BSI IT-Grundschutz Compendium, module NET.1.1 Network architecture and design (German), requirement NET.1.1.A23
- Collaboration between several Microsoft 365 tenants: Microsoft Learn – Multitenant organization capabilities in Microsoft Entra ID
- Moving mailboxes between tenants: Microsoft Learn – Cross-tenant mailbox migration
IT for an office move: what to plan and when
Planned backwards from the day of the move: internet connection and lead times, phone numbers, cabling, server, firewall and printers, plus the order on the day and what still follows afterwards.
Read article→
3CX or Teams Phone: which cloud phone system suits your business?
When I recommend 3CX, when Teams Phone, what a cloud phone system costs per workstation and where a switch can go wrong: lessons from around 20 phone systems I have set up.
Read article→
Server move in one day: what needs planning beforehand
A project from 2025: a new server, a new domain and every workstation moved across in one day. What has to happen beforehand, what the schedule and fallback plan look like, and where the time really goes.
Read article→