How to secure Microsoft 365: the key settings for small companies
Which Microsoft 365 settings come first, which licence they need and what is possible without Business Premium. An overview for managing directors and the people responsible internally.
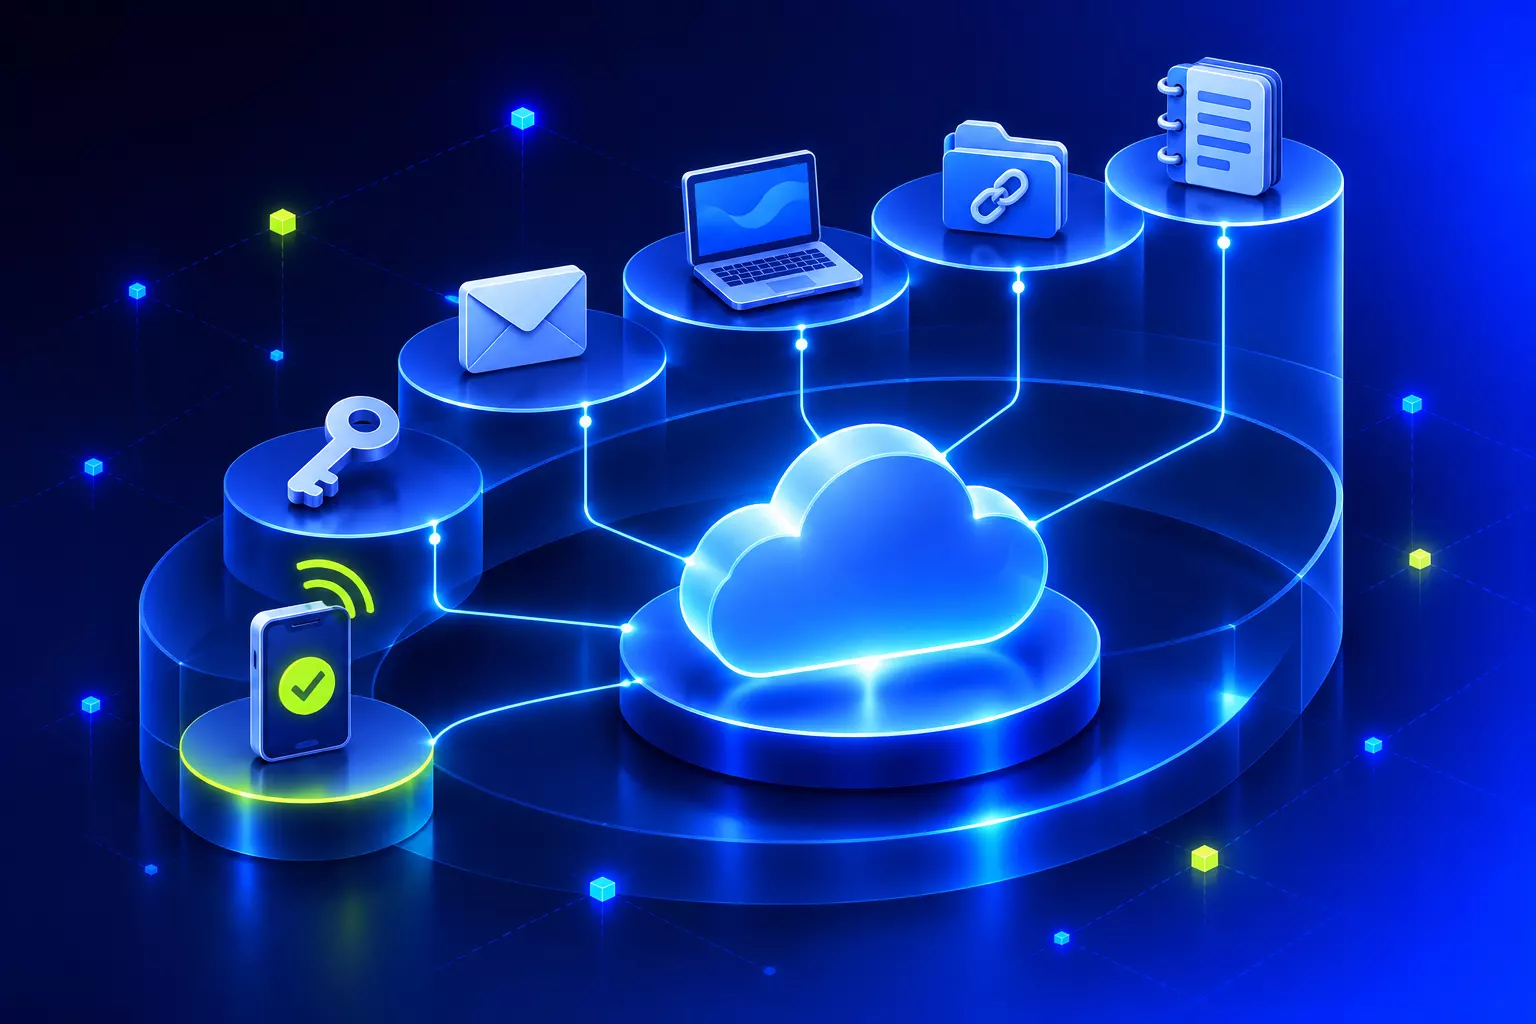
To secure Microsoft 365, what matters most is setting a few things deliberately and in the right order. Many of them need no add-on licence. This overview shows managing directors and the people responsible internally what comes first and which licence it takes. It is not a click-by-click guide.
How to secure Microsoft 365: what comes first?
- Sign-inmulti-factor authentication for everyone, legacy sign-in blockedFirst
- Admin accountsfew, separate from everyday work, two emergency access accounts
- Emailsecurity policies, SPF, DKIM, DMARC, no automatic external forwarding
- Devicesmanaged, encrypted, with endpoint protection
- Sharing and appsclear rules for external links and for app consent
- Audit log and backuptracing what happened and getting data back
The first four levels match the first four points in Microsoft’s security best practices for businesses with up to 300 users. Sign-in comes first because a compromised account renders many of the other safeguards useless.
Sign-in: multi-factor for everyone
According to Microsoft, multi-factor authentication can block more than 99.2 per cent of attacks on accounts. Legacy sign-in methods should be switched off at the same time, because they can be used to bypass the second factor.
Without Business Premium, Microsoft’s security defaults take care of this. They have been active by default in tenants since October 2019, but they can be switched off. So check whether they are running in yours. With Business Premium I replace them early on with Conditional AccessRules that determine who may sign in, from which device and location, and with which sign-in method.. I explain why in the article on the security features of Business Premium.
Plan for everyday life afterwards too. Among the clients I look after, it happens that someone replaces their phone and their sign-in has to be reset. Settle beforehand who will handle that.
Admin accounts: few and separate
- Few: Microsoft recommends fewer than five global administrators.
- Separate: administrators use a normal account for everyday work and the admin account for administration only.
- Emergency access accounts: two cloud-only accounts secure the way back into the tenant.
None of this needs an add-on licence. How roles can be limited to being active only for a set time, and which licence that takes, is covered in the article on Privileged Identity Management.
My principle: only the emergency access accounts are permanently Global Administrator. In-house and external IT obtain their roles through PIM as and when they need them, and do not hold them permanently. PIM requires Entra ID P2 or ID Governance, which Business Premium does not include.
Email: policies, SPF, DKIM and DMARC
- Preset security policies: Microsoft offers the Standard and Strict levels. They apply recommended values without anyone having to maintain each setting individually. Basic and Standard include baseline protection against spam, malware and phishing. Safe Links and Safe Attachments are only available with Defender for Office 365, so in Business Premium or as an add-on.
- SPF, DKIM and DMARC: these DNS records make it harder to send forged email in your name. They belong on every domain you own, including unused ones. For DMARC, Microsoft advises a gradual rollout: monitor first, then send to quarantine, and finally reject.
- Automatic external forwarding: a compromised account can also use this to forward email outside the company. The default value behaves differently depending on the tenant. Microsoft therefore recommends explicitly switching forwarding off and handling any necessary exceptions deliberately.
Devices: managed, not just signed in
Basic and Standard include simple management for mobile devices in the form of Basic Mobility and Security. Intune and Defender for Business only come with Business Premium. They let you control encryption and updates centrally and, together with Conditional Access, make access depend on the state of the device. There is more in the article on device management in business.
For personal devices I recommend a clear rule: either company devices only, or on personal devices just mail and Teams with app protection.
Sharing and apps: what may leave the company
External sharing is allowed by default in SharePoint and OneDrive, and Microsoft advises leaving it on. That is usually better than files in emails or personal cloud services. The real issue is links that need no sign-in: a forwarded link also works outside the company, and nobody can see who opened the file. Microsoft recommends not allowing these links, or at least giving them an expiry date and limiting them to viewing. This is how I set it up: guests with sign-in, anonymous links off.
Apps are similar. By default, staff can give an app access to their own data, such as their mailbox. Microsoft recommends limiting this to apps from verified publishers.
Audit log and backup
According to Microsoft, the audit log is not switched on from the start in Business Basic, Standard and Premium. It records many important activities of users and administrators and, with standard audit, usually keeps the entries for 180 days. After an incident it lets you trace what happened. The log comes late in the order, but you should not put off switching it on.
None of these settings brings back deleted or encrypted data. That takes a separate backup, see Does Microsoft back up my data?
What is possible with which licence?
| Measure | Basic | Standard | Premium |
|---|---|---|---|
| Security defaults | ✓ | ✓ | ✓ |
| Conditional Access (Entra ID P1) | – | – | ✓ |
| Baseline protection for email | ✓ | ✓ | ✓ |
| Safe Links and Safe Attachments (Defender for Office 365 Plan 1) | – | – | ✓ |
| Simple management of mobile devices (Basic Mobility and Security) | ✓ | ✓ | ✓ |
| Intune Plan 1 | – | – | ✓ |
| Defender for Business | – | – | ✓ |
Possible without an add-on licence: SPF, DKIM, DMARC, forwarding, sharing, app consent and the audit log. PIM is not included in any of the three licences. Source: Microsoft Learn, as of October 2026.
How well is your Microsoft 365 secured?
How I go about it
- Assessment: I read out the settings and review them. What comes out of this is described in the article on the Microsoft 365 audit.
- Rollout: I announce noticeable changes in advance and support the switch, on site if necessary. I get hardly any queries afterwards. If anything, I go over rarely used features again, such as a mail archive.
- Operation: if you like, I can take over day-to-day operation as part of IT support.
I do not quote a flat figure for the effort, because environments and requirements differ too much.
Frequently asked questions
Microsoft already requires multi-factor authentication. Isn’t that enough?
No. Microsoft’s requirement applies to signing in to admin portals such as the Microsoft 365 admin center. For normal access to mailboxes and files, you have to enforce multi-factor authentication yourself.
Are security defaults enough for a small company?
As baseline protection, yes. Microsoft considers them suitable for most organisations. But they can only be switched on or off and cannot be adjusted. If you need rules by device or location, you need Conditional Access and therefore at least Entra ID P1.
Can I secure Microsoft 365 without moving to Business Premium?
Partly. Many points in this article are also possible with Basic and Standard, and the table above shows the limits. If you want to manage devices centrally or make access depend on conditions, you cannot avoid add-on licences. That is why Business Premium is my standard.
What is not worthwhile for small companies, or only later?
Sentinel and security operations, E5, elaborate compliance packages and large-scale data classification. The basics in this article come first.
Sources
- Recommendations and licences: Microsoft Learn – Microsoft 365 for business security best practices, Microsoft Learn – Microsoft 365 for business security overview (as of October 2026)
- Sign-in: Microsoft Learn – Security defaults in Microsoft Entra ID, Microsoft Learn – Set up multifactor authentication for Microsoft 365, Microsoft Learn – Mandatory multifactor authentication (as of October 2026)
- Admin accounts: Microsoft Learn – Best practices for Microsoft Entra roles, Microsoft Learn – Manage emergency access accounts (as of October 2026)
- Email: Microsoft Learn – Preset security policies, Microsoft Learn – Get started with Microsoft Defender for Office 365, Microsoft Learn – Set up DMARC, Microsoft Learn – Control automatic external email forwarding (as of October 2026)
- Sharing: Microsoft Learn – Plan sharing and collaboration options, Microsoft Learn – Manage sharing settings, Microsoft Learn – Secure external access to Teams, SharePoint and OneDrive (as of October 2026)
- App consent: Microsoft Learn – Configure how users consent to applications (as of October 2026)
- Audit log: Microsoft Learn – Turn auditing on or off, Microsoft Learn – Search the audit log (as of October 2026)
Employee training with Campus: mandatory training, onboarding and records in one place
Data protection training, phishing, new employees: how Campus organises mandatory training with deadlines, onboarding and records for small companies, from the reminder to the annual report.
Read article→
PHP2Shell: is my website affected by the PHP vulnerability?
Two critical vulnerabilities in PHP threaten millions of websites, and updating WordPress does not help. Who is affected, why a patch alone is not enough and how I check your website.
Read article→
Hornetsecurity for Microsoft 365: when additional email security makes sense
Why I usually add Hornetsecurity for email protection when clients use Business Standard, how the switch works, and when I recommend Business Premium instead.
Read article→